

While many SAP customers are transitioning to S/4HANA, the majority still rely on conventional database platforms, with Oracle remaining one of the most common choices. Poorly configured Oracle databases can act as a major attack vector, allowing threat actors to bypass application-level security and compromise sensitive SAP data directly at the database layer.
Why is securing Oracle databases for SAP critical?
Oracle databases include robust security features such as network encryption, transparent data encryption, and granular access control (Database Vault). However, these features are only effective when properly configured. Attackers frequently target misconfigured databases to gain unauthorized access, effectively circumventing the security controls built into the SAP application itself. To mitigate these risks, organizations must adopt a hardened configuration strategy that addresses both system parameters and user privileges.
What are the best practices for Oracle database hardening?
Securing an Oracle database supporting SAP requires specific configuration changes to reduce the attack surface:
- Disable the OPS$ mechanism: Set the
REMOTEOSAUTHENTparameter toFALSEto prevent unauthorized remote logins using externally authenticated OS users. - Restrict sensitive parameters: Use parameters like
07DICTIONARYACCESSIBILITYto limit SYS schema access,globalnamesto block unauthorized domains, andremotelogin_passwordfileto prevent password file authentication. - Manage default accounts: Change default passwords for all standard Oracle users immediately after installation. Refer to the Oracle Help Center for the full list of standard users.
- Limit PUBLIC group access: Revoke execution rights for sensitive packages such as
UTLORAMTS,UTLHTTP, andHTTPURITYPEfrom the PUBLIC group. - Restrict high-level privileges: Avoid granting
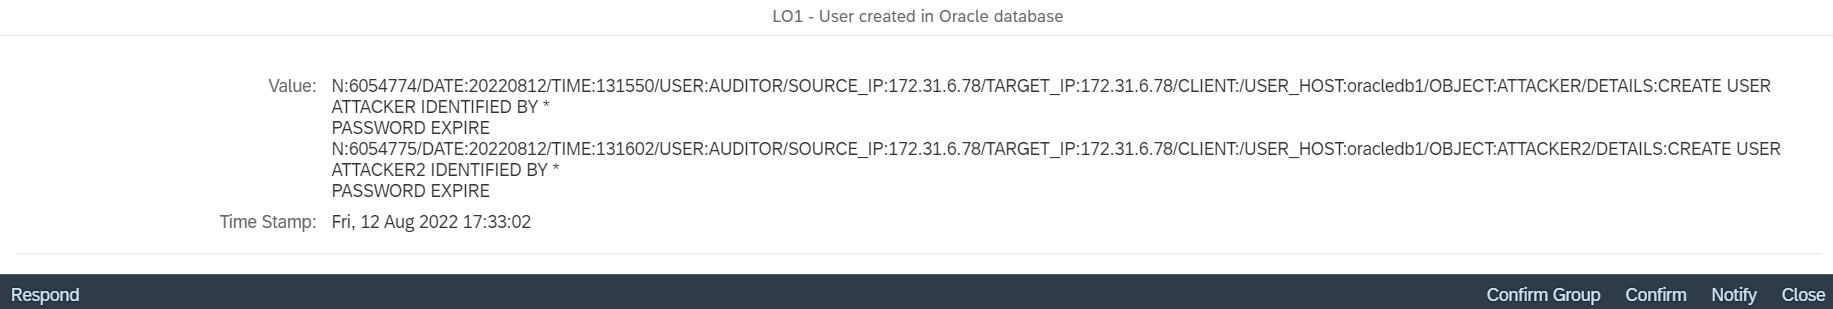
WITH_ADMINprivileges and restrict critical system privileges likeALTER SYSTEM,GRANT ANY PRIVILEGE, andBECOME USERto only authorized users. - Implement auditing: Enable logging for sensitive events, including role/user changes, modifications to stored procedures, and alterations to the audit trail in
SYS.AUD$.
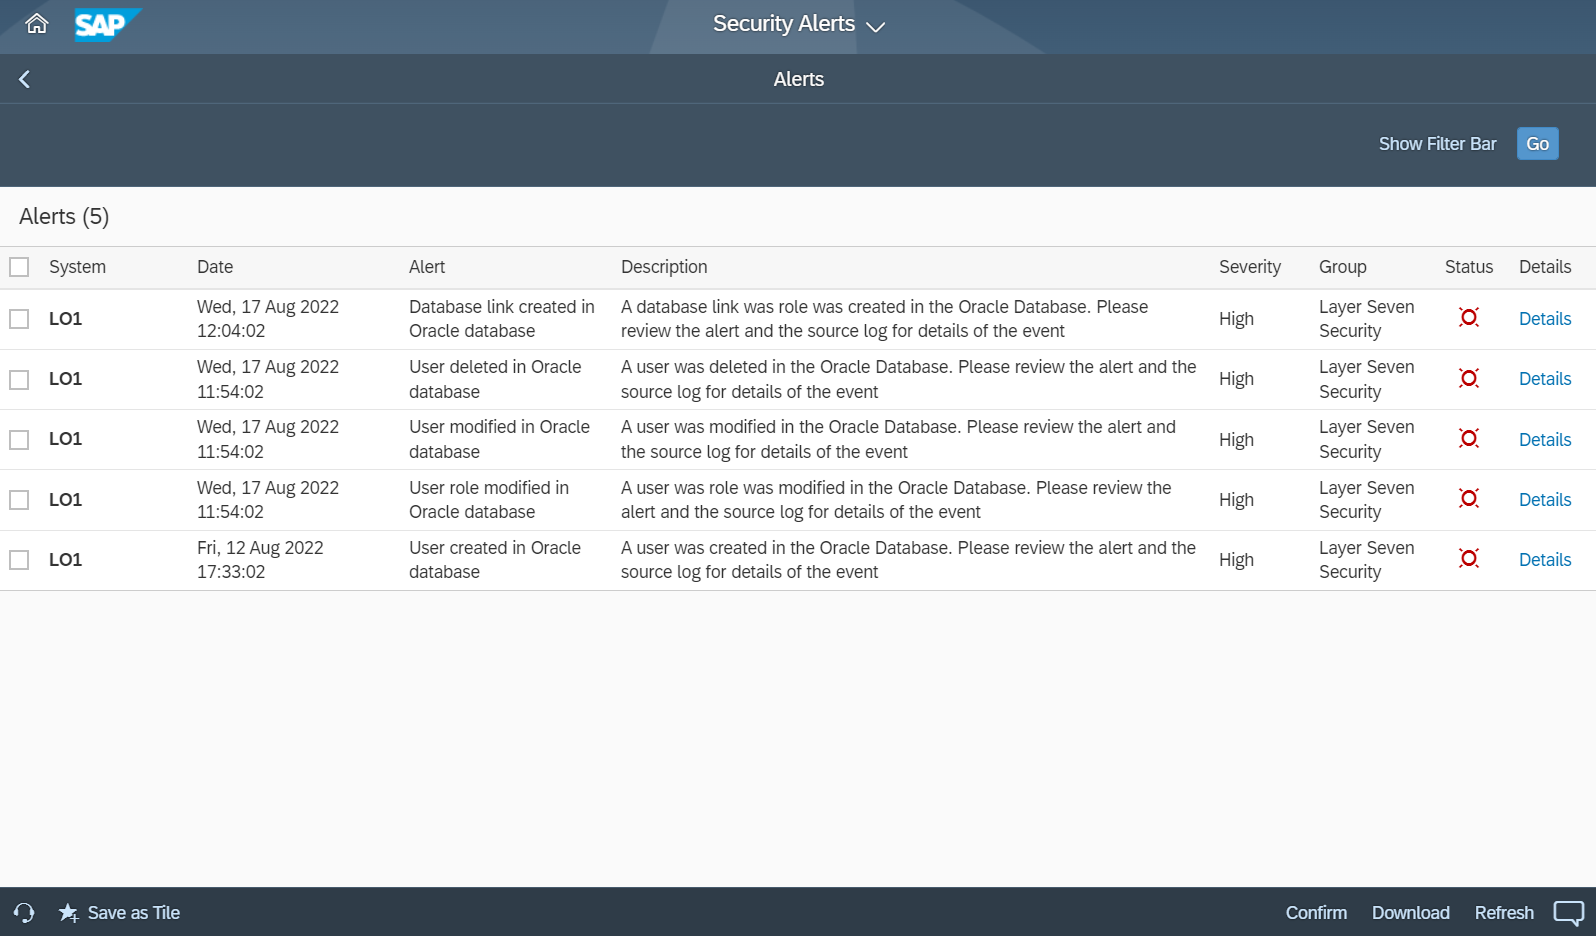
How does the Cybersecurity Extension for SAP (CES) simplify database security?
The Cybersecurity Extension for SAP (CES) provides automated vulnerability scanning specifically designed for Oracle databases in SAP environments. This SAP-certified add-on detects critical misconfigurations, insecure authentication mechanisms, and users with excessive privileges that standard scans might miss.
CES Database Security Features
| Feature | Description |
|---|---|
| Vulnerability Scanning | Detects insecure authentication and database misconfigurations. |
| Privilege Analysis | Identifies users with critical roles and excessive system privileges. |
| Audit Monitoring | Audits configuration compliance and incomplete audit policies. |
| Threat Detection | Monitors database logs for security incidents and potential breaches. |
Frequently Asked Questions
Why should I disable the OPS$ mechanism in Oracle?
The OPS$ mechanism allows users to log in to the database using OS-level credentials, which can be exploited by threat actors for unauthorized remote access. Disabling this by setting REMOTEOSAUTHENT to FALSE is a critical security step for modern SAP environments.
What are the risks of leaving PUBLIC group permissions unchanged?
The PUBLIC group includes all database users. If sensitive packages like UTL_HTTP are left executable by PUBLIC, any database user could potentially send sensitive data to external, unauthorized destinations.
Does the Cybersecurity Extension for SAP cover the entire SAP stack?
Yes, CES is the only solution that secures the entire SAP stack, including the application layer, the database layer, and the host operating system, including Oracle Linux, Red Hat Enterprise Linux (RHEL), and SUSE Enterprise Linux Server (SLES).